Security & IAM
Guardrails for people and agents.
Every request — from a person, from Molly or through the API — is checked against org, role, team and per-record grants, with field-level enforcement and a role hierarchy managers inherit through. Agents work inside a monthly budget and queue what needs a person for approval. An append-only audit log keeps the record, and every feature has a switch.
- OpenFGA-backed authorization
- ReBAC
- system and custom roles
- 4 + ∞
- audit retention
- 45 days
- authenticator app or email OTP
- 2FA
Access model
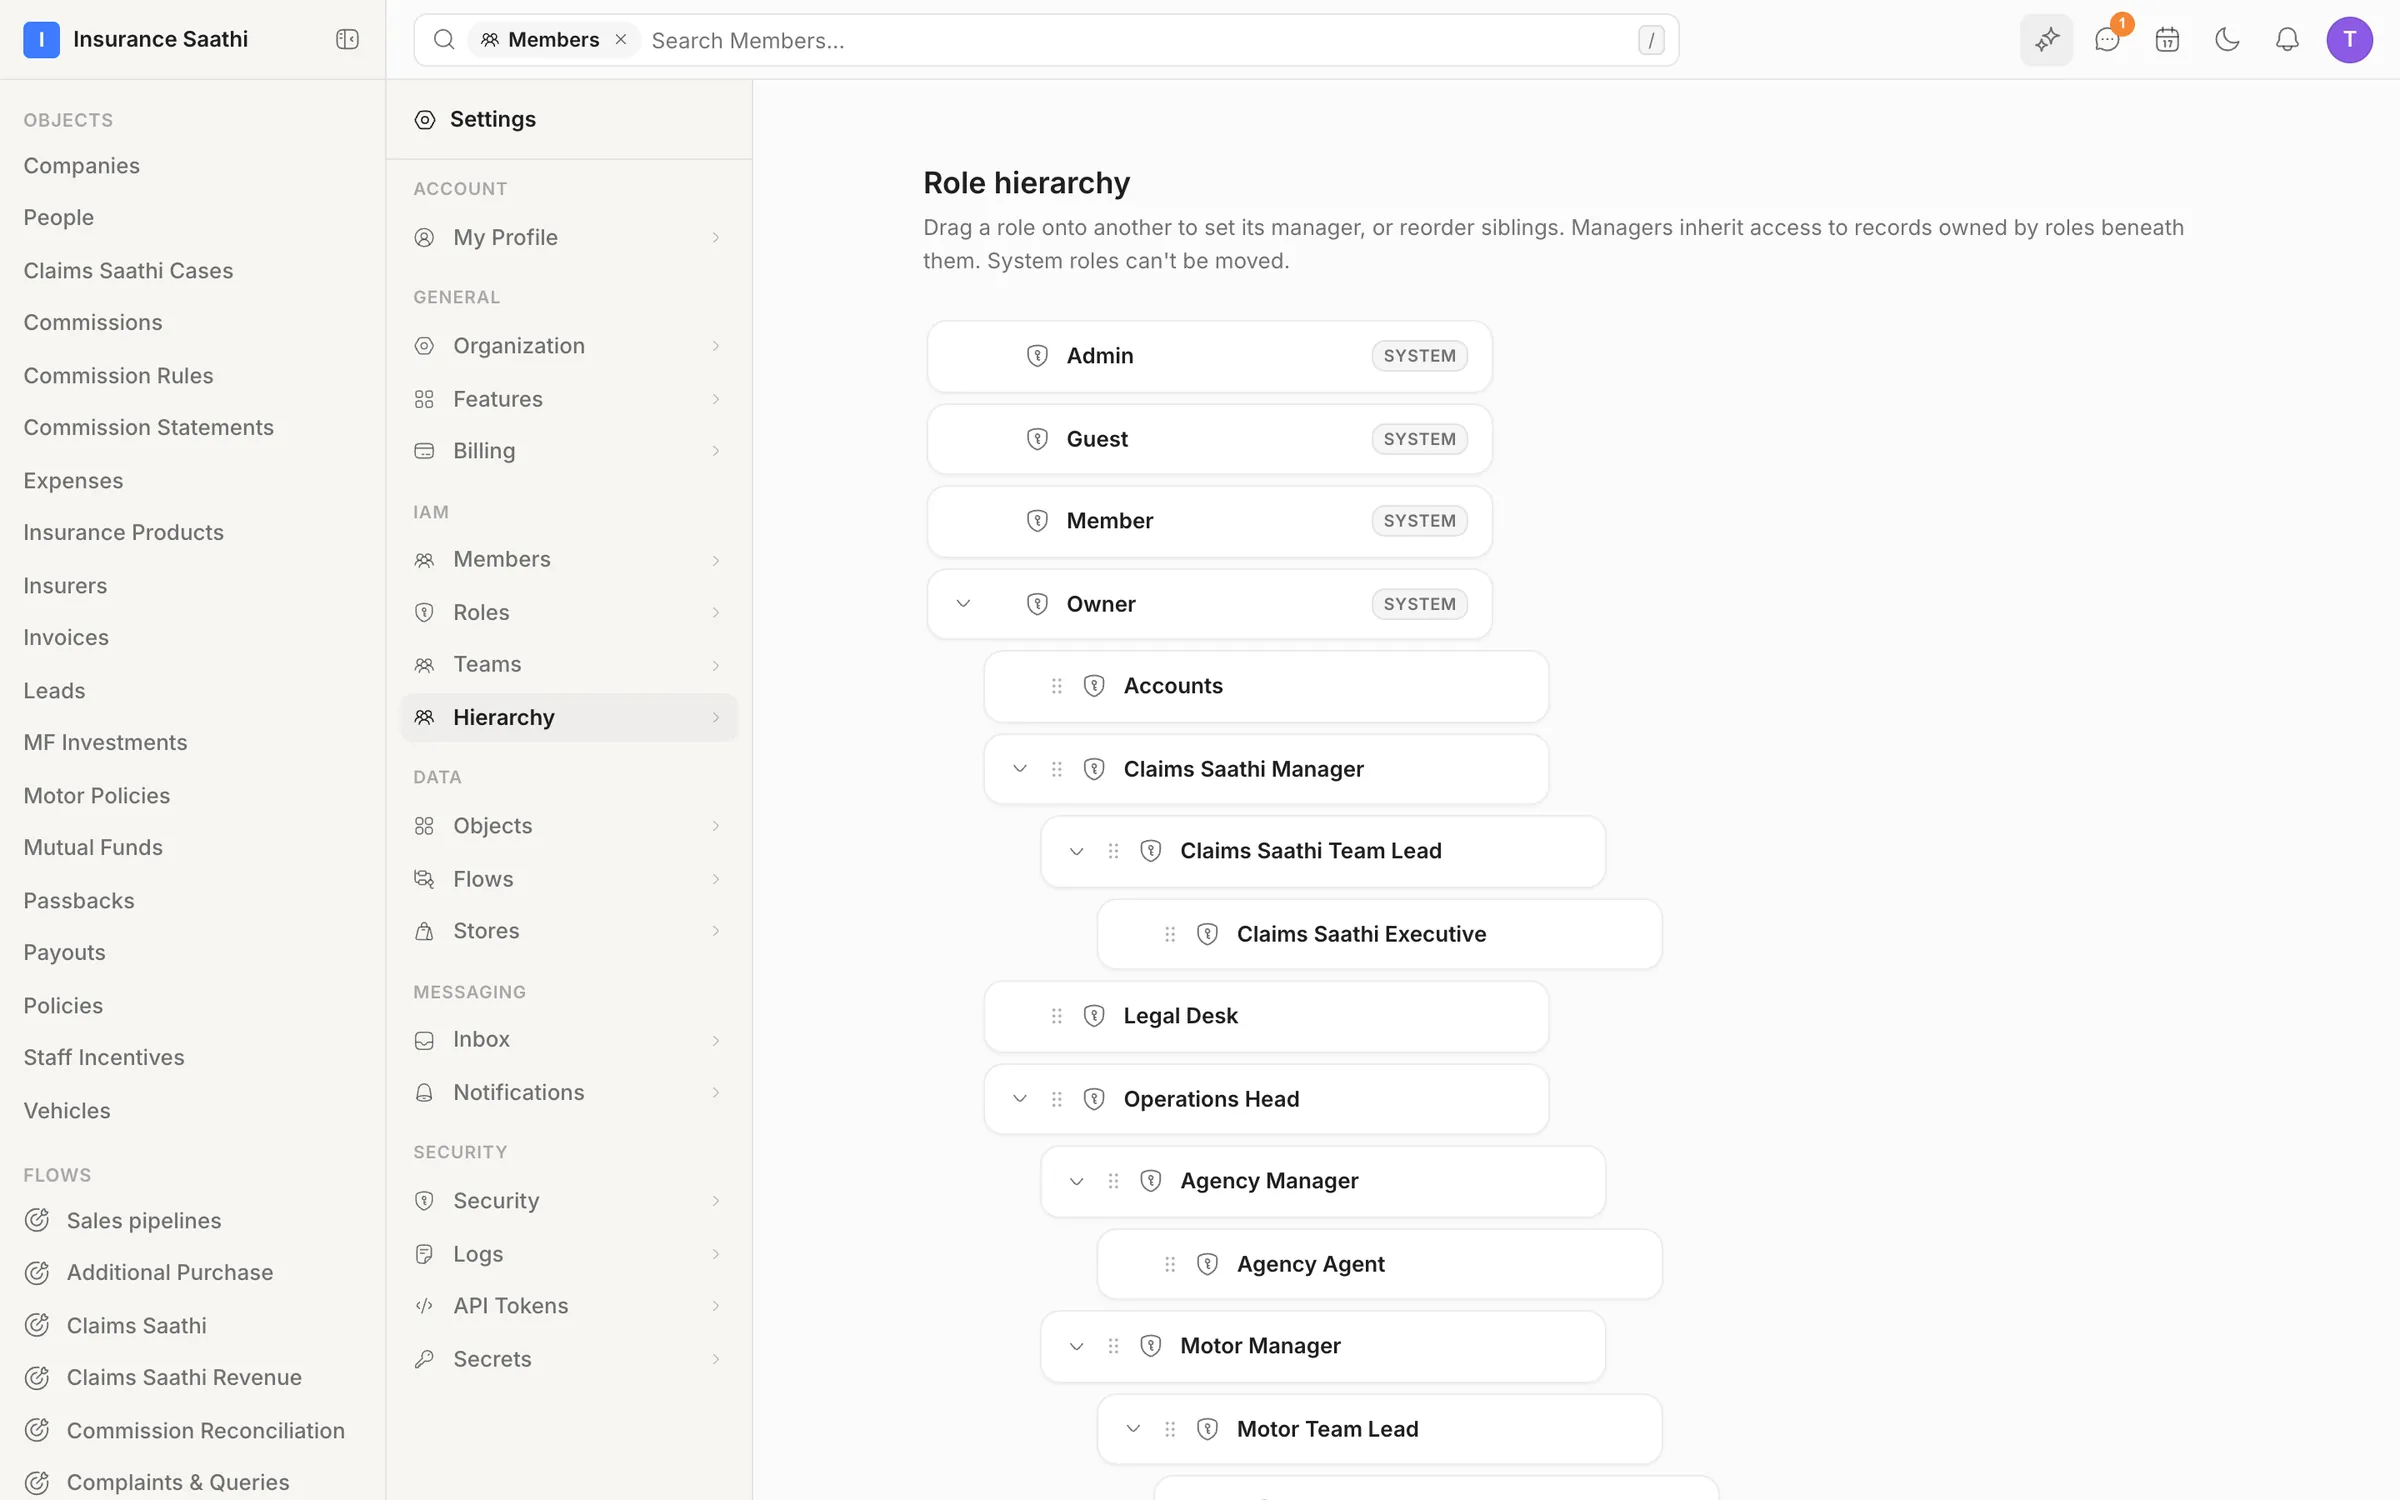
Access that follows your org chart
Four system roles — Owner, Admin, Member and Guest — plus custom roles that define what each can do across objects, fields, features and system capabilities. Drag a role onto another to make it the manager; managers inherit access to records owned by the roles beneath them.
- Custom roles that inherit from a parent
- Teams for shared access — one person, many teams
- Guests see only the Team Inbox threads they're in
Record & field security
Who sees what, down to the field
Org-wide defaults set the baseline per object — private, read or read-write. Shares grant access to a user, team or role per record. Field permissions hide or lock individual fields — enforced identically in the UI, the query engines and the API.
- Org-wide defaults per object type
- Per-record sharing to user, team or role
- Field read, write and hidden enforcement
Audit
A record of who did what
Logins, record access, changes, exports and admin activity stream to an audit and access log you can filter by category, action, user, status and date — retained 45 days and exportable to CSV.
- Security, auth, data and admin categories
- Denied-access events captured too
- Export CSV for compliance workflows
Governance
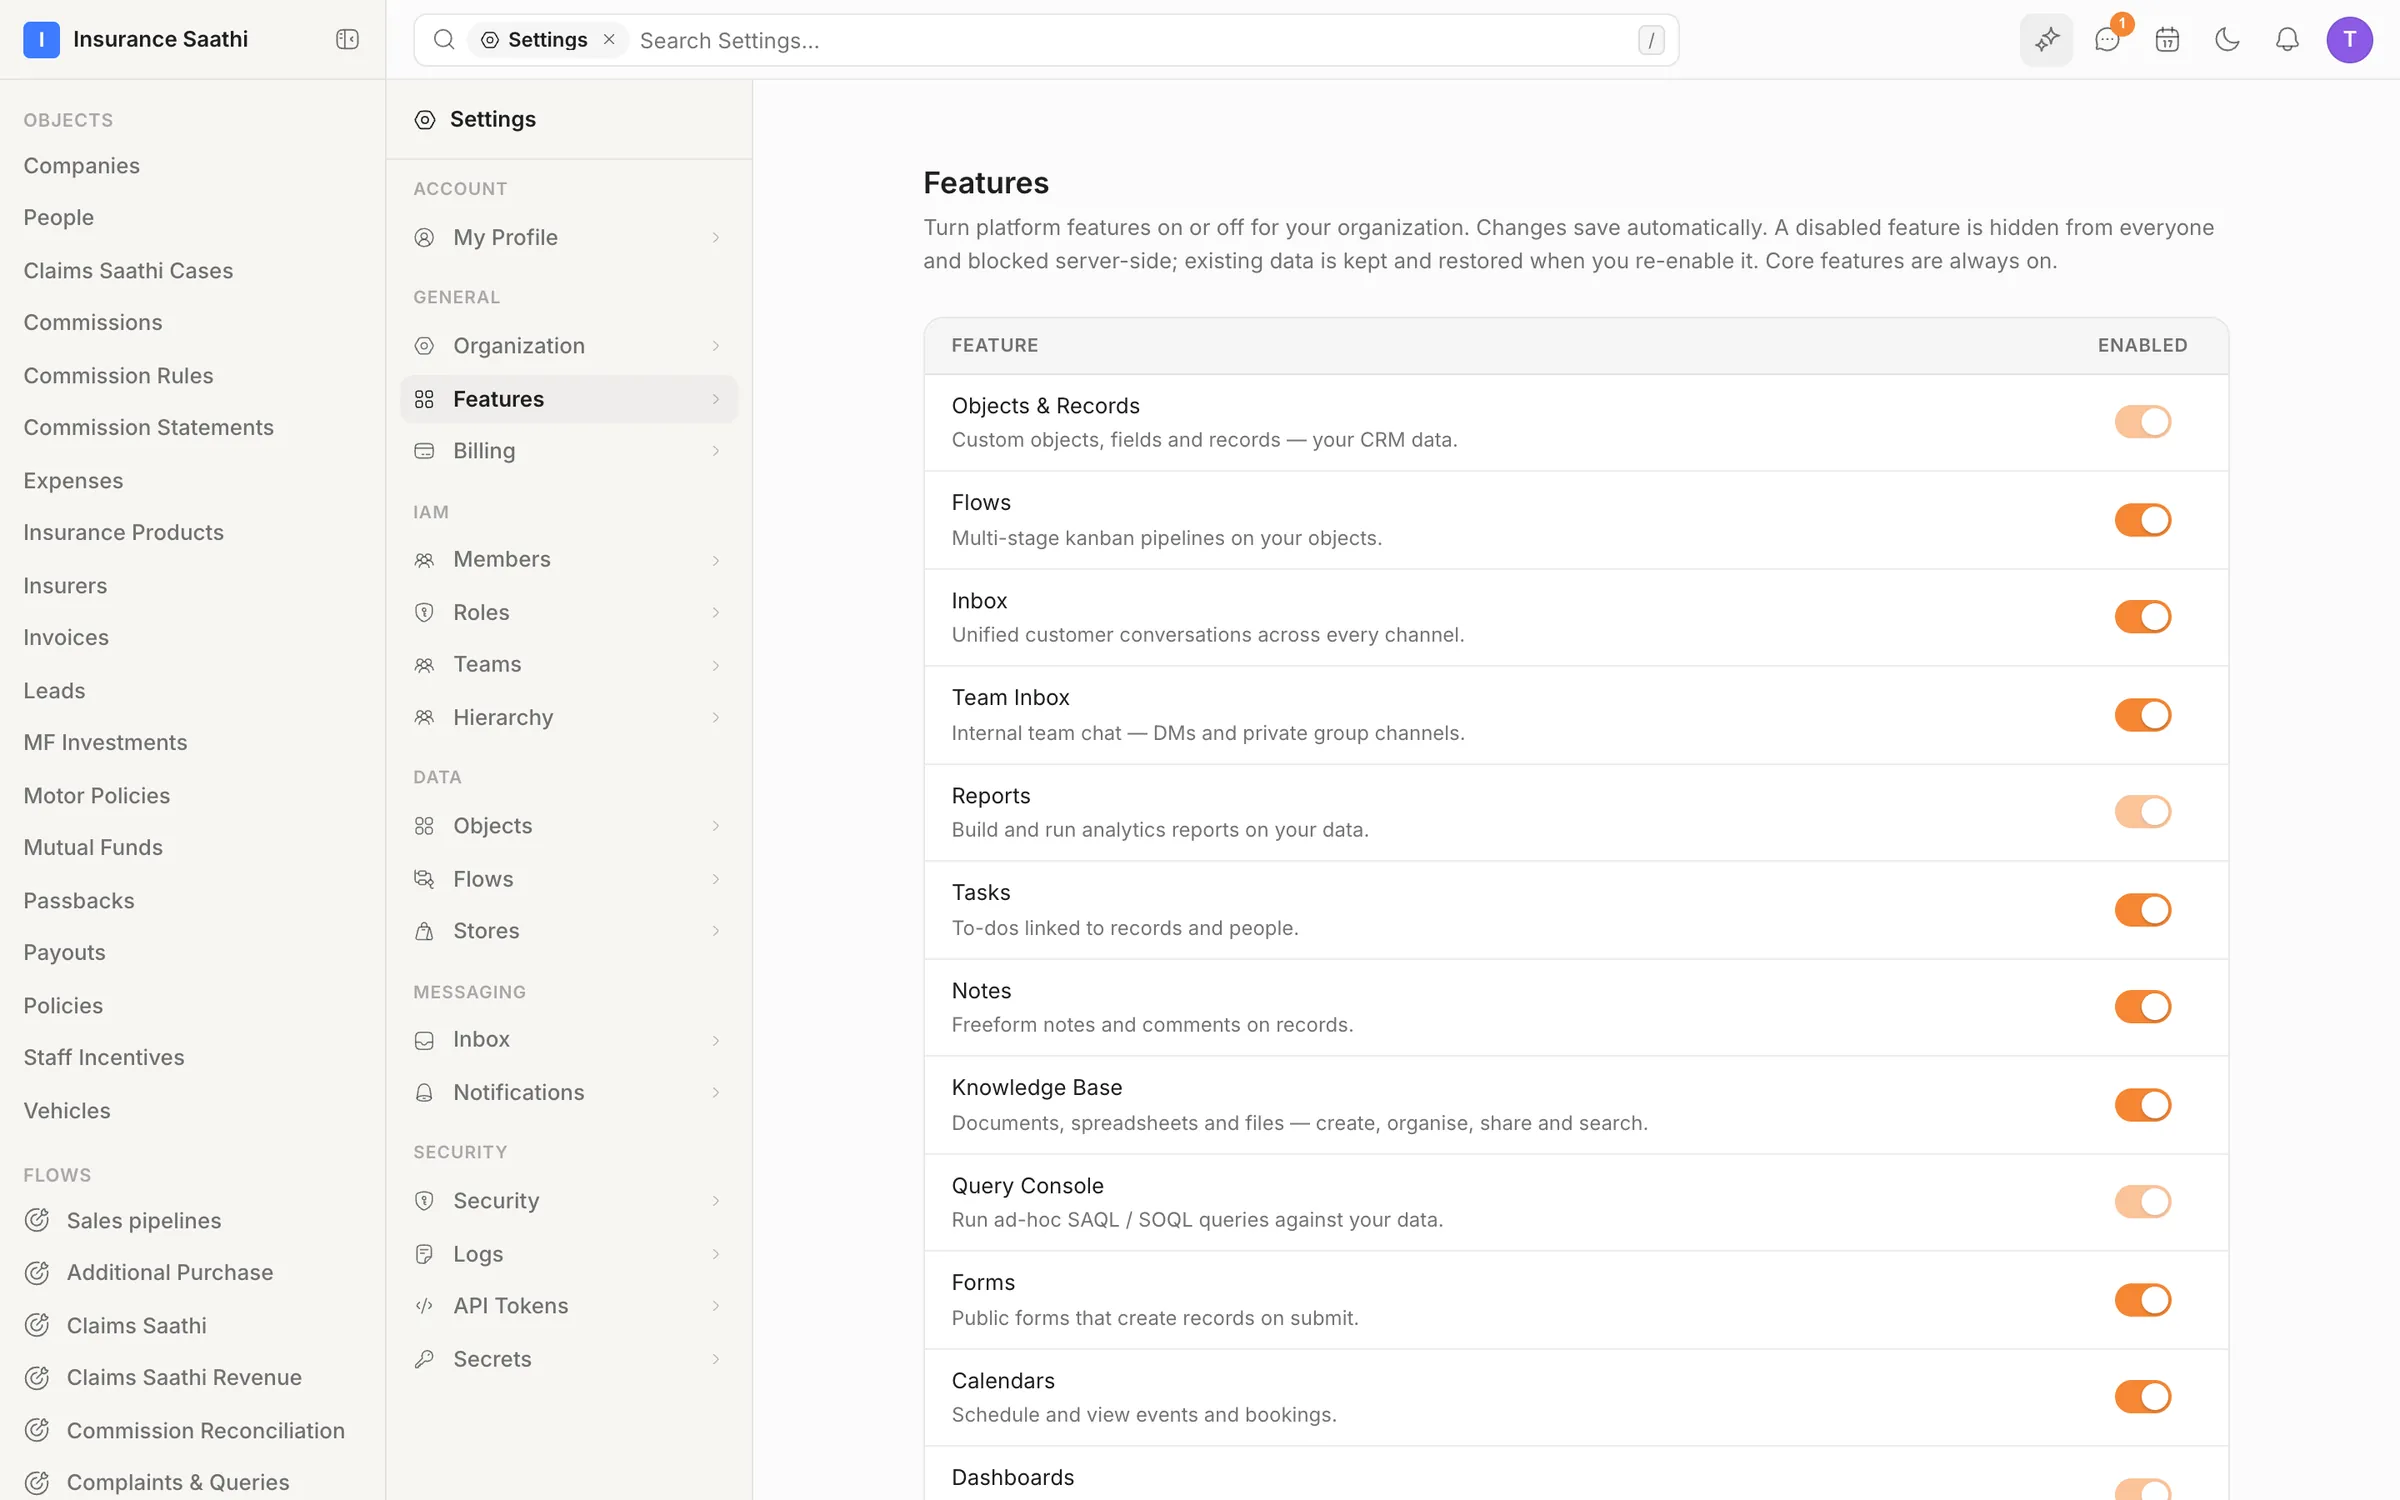
A switch for every feature
Turn features on or off for the whole organisation — flows, the inbox, chatbots, broadcasts, AI agents and more. A disabled feature is hidden from everyone and blocked server-side; its data is kept and restored when you switch it back on. Core features are always on.
- Enforced at the API, not just hidden in the UI
- Data kept while a feature is off
- Core features locked on
Also in the box
Two-factor sign-in
An authenticator app or email OTP as a second factor, with trusted devices that expire after 30 days.
Search access policy
Choose who can query what: the whole org, restricted, or admins only.
Secrets Vault
Encrypted, write-only values for agent sandboxes; outputs are redacted.
API tokens
Bounded by the scopes you pick and your live permissions — never more than your account.
Materialised ACLs
Access denormalised onto records for fast, scoped search and analytics.
Soft delete
Records survive accidents; deletion is a state, not an event.
Put your agents to work.
Bring your team, connect your channels and let klerc take the follow-ups — from first hello to paid invoice.
Free during early access. No credit card needed.